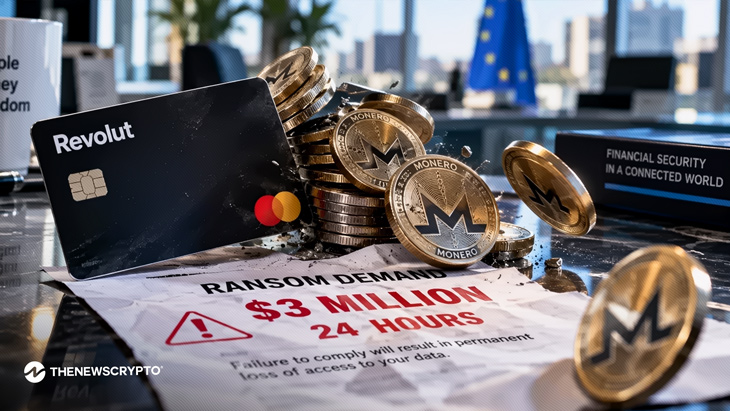
- The hackers now demand around $3 million in Monero within 24 hours, having earlier demanded a 10,000 BTC ransom.
- The hackers say that the data of 680 customers includes IDs, bank accounts, and cryptocurrency transactions.
The attackers responsible for the Revolut data breach now have a demand of 3 million dollars in Monero. The IAmNotAVillain group reportedly demands 6,000 XMR within 24 hours. This is to sell the customers’ data to any criminal organization if Revolut rejects the demand. This has been replaced by a demand of 10,000 BTC, which had been previously shared on Telegram. According to the Financial Times, Monero provides better anonymity than Bitcoin. While Monero transactions cannot be traced because of the anonymity of the transacting parties, Bitcoin transactions are publicly traceable via the blockchain ledger.
A group of hackers claims to have spent months posing as a law enforcement entity from Italy to obtain confidential data on hundreds of Revolut customers. https://t.co/h55J7wobDQ pic.twitter.com/Wv7R8gUWSk
— Financial Times (@FT) September 15, 2026
Government Phishing Scam Exposes 680 Clients
The attack started after hackers apparently used an authorized government email box to issue phony information requests. Requests were processed by the compliance team of Revolut following successful SPF, DKIM and DMARC checks. Affected clients were notified about the hack on September 12 after the company detected the sophisticated phishing attack. Exposed data is said to include passports, driving licenses, verification selfies, and contact information. It also comprises IBANs, account statements, withdrawals, and full transaction histories related to Bitcoin. The actor says that he targeted crypto owners for months via blockchain analysis.
Customers with considerable crypto assets were identified based on their Revolut accounts. The hacker says 680 clients have been compromised, of which most are located in Switzerland and France. Others are reportedly from 31 other mostly European nations, including Britain, Germany and Spain. The hacker also says he owns 147 GB of Italian law enforcement files. The Italian authorities have not verified any breach involving police databases.
Investigations are Continuing by Regulators
The Information Commissioner’s Office of the United Kingdom reviewed the report filed by Revolut concerning the data breach. The Financial Conduct Authority of the country confirmed engagement with the company regarding the data breach incident. The investigation is also ongoing, with the involvement of Italian police and the Interior Ministry, concerning the alleged hack into the government’s email account of the government. Revolut has blocked the phishing account, and the firm informed all concerned authorities of the issue.
The details shared through the breach notification did not include any details like private keys, card PIN numbers, or account balances. The European banking unit of Revolut Bank UAB comes under the regulation of the ECB and the Bank of Lithuania.
Highlighted Crypto News:
ECB Seeks Euro-Area Merchants to Test Digital Euro Payments in 2027