- India’s CERT-In identified CRAFTY FALCON in an active AI-assisted cyberattack campaign targeting crypto exchanges and financial firms.
- The agency reported crypto wallet key theft and fund transfers, warning organisations to strengthen cloud security, API monitoring and wallet protection.
India’s cybersecurity agency CERT-In has issued a critical warning about an active hacking campaign targeting cryptocurrency exchanges and financial institutions, with attackers using artificial intelligence (AI) tools to steal wallet keys and transfer funds.
In its November 4 advisory, identified as CIAD-2026-0058, the Indian Computer Emergency Response Team named the threat actor “CRAFTY FALCON” and said the attacks were continuing to escalate. The campaign also targets non-banking financial companies (NBFCs), digital lending platforms, fintech firms, payment aggregators and payment service providers.
🚨 BREAKING: India’s CERT-In warns that AI-powered hackers are targeting crypto exchanges, stealing wallet keys and siphoning funds. The agency identified the threat actor as “CRAFTY FALCON” and said the attacks remain active and escalating. CERT-In has urged exchanges to strengthen security and maintain 24/7 monitoring. #CERTIn #CyberSecurity #Crypto #India
— TheNewsCrypto (@The_NewsCrypto) November 5, 2026
CERT-In said its financial-sector response team, CSIRT-Fin, had received reports of successful attacks, including against organisations that had already been warned and attempted to fix security weaknesses. Some were targeted again after incomplete remediation, while attackers timed operations around weekends and holidays when security teams may have fewer staff monitoring systems.
Four AI tools identified in the campaign
The advisory names four publicly available tools used in the attacks: ARTEX, PentAGI, Cairn and CyberStrikeAI. According to CERT-In, these tools can automate attack sequences, generate and refine customised scripts, and adjust their methods based on how target systems respond. The attackers also rotate their supporting infrastructure’s IP addresses within hours or days, making detection more difficult.
The agency described several methods used to break into financial systems. Attackers have exploited exposed testing environments, misused cloud services and made unauthorised requests to payment APIs through modified applications. In some cases, they sent small test payments, including transactions worth just ₹1, to check whether unauthorised transfers would work before attempting larger amounts.
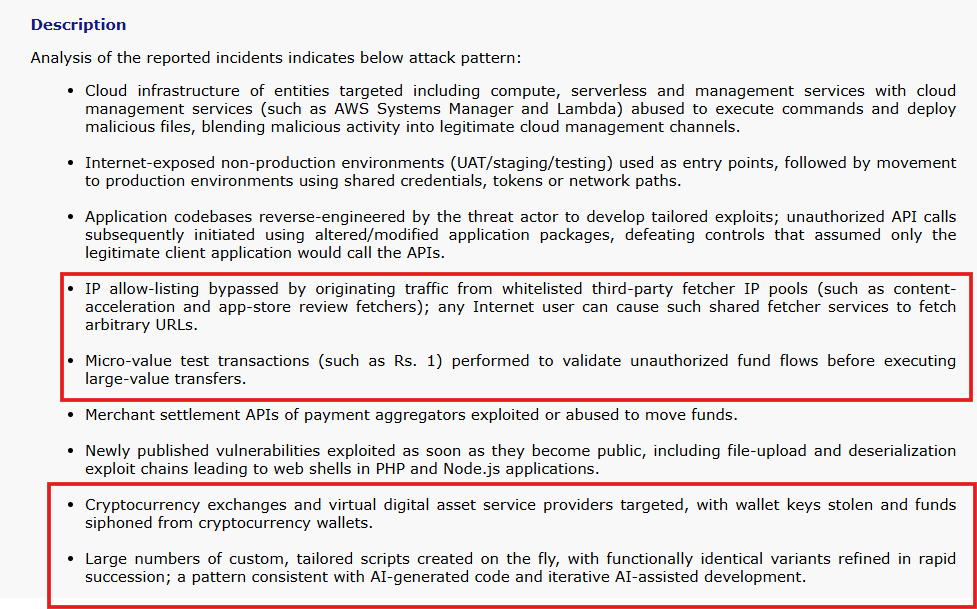
CERT-In specifically reported that cryptocurrency exchanges and virtual digital asset service providers had been targeted, with wallet keys stolen and funds siphoned from wallets. However, the advisory did not identify affected exchanges or disclose the total amount stolen.
The agency has urged financial firms to maintain round-the-clock security monitoring, strengthen transaction checks and store crypto wallet keys in hardware security modules or cold storage. It also recommended multisignature approval for withdrawals and immediate key rotation if a compromise is suspected.